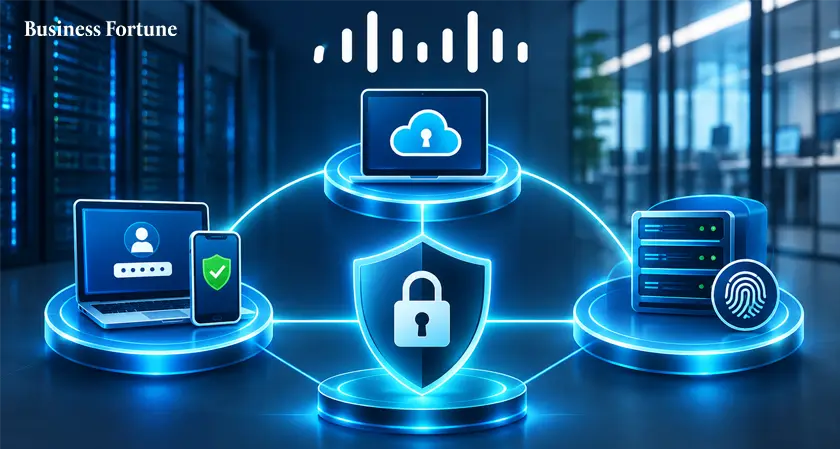
Cisco Access Security Solutions cover cloud, identity and network enforcement. Here is what each product does and where enterprises use it.
Cisco Access Security Solutions overview
The Cisco Access Security Solutions are based upon three products: Secure Access (cloud SSE solution), Duo (identity & access management solution) and Identity Services Engine (policy engine for Network Access Control). These solutions are based within their zero trust framework.
Together these will determine who is trying to connect, with what device, to what resource. However most are based around a feature rich overview. We have outlined how these solutions will apply at certain points within the access journey.
What is Cisco Access Security?
The access security solution is based around 4 individual Cisco security technologies that can enforce policies at the login, network port and cloud edge. This is augmented with Identity Intelligence to monitor the identity. The table below outlines the 4.
|
Product |
Where it enforces |
Core capabilities |
Typical starting point |
|
Cisco Secure Access |
Cloud edge, between users and the web, SaaS and private apps |
ZTNA, secure web gateway, CASB, firewall as a service, DLP, DNS-layer security, VPN as a service |
Hybrid and remote workforce |
|
Duo |
Identity layer, at login |
Phishing-resistant MFA, SSO, passwordless, Trusted Endpoints, adaptive policies |
Workforce authentication |
|
Identity Services Engine |
Network edge: switch port, wireless, VPN |
802.1X, MAC Authentication Bypass, posture, profiling, guest access, TrustSec segmentation |
Campus and branch networks, including IoT |
|
Cisco Identity Intelligence |
Across identity sources |
Visibility into MFA use, dormant accounts and excess permissions; threat detection |
Identity posture and threat detection |
As seen above Duo will make decisions at login, ISE will make decisions at switch/ wireless association/VPN and Secure Access will make decisions at web traffic, SaaS or Private applications. Cisco's access control solutions complement rather than replace one another.
How does Cisco Secure Access help secure enterprise users?
Secure Access provides an integrated solution offering Zero Trust Network Access, secure web gateway, Cloud Access Security Broker, Firewall as a service, Data Loss Prevention, DNS Layer Security and Remote Browser Isolation. All of these are managed from a single console using a single set of policies. Users will connect using the Secure Client.
Zero Trust Network Access will block by default. When trying to connect to a private application this will be allowed based on policies. These policies will ensure least privilege access is applied and using a client or clientless approach, including unmanaged devices. If an application cannot be used with ZTNA then the user will fall back to using a VPN as a service. Talos research powered and using hyper scaler and Cisco managed points of presence.
The release notes provide more detail. A weekly update log is provided and recent updates have focused around governance. This includes exclusive edit lock to ensure only one administrator can save conflicting changes to Access Policies, rule comments, country conditions on access rules and searchable logging for Resource Connectors. On the 30th October 2026 Secure Client 5.1.19 now supports Zero Trust Access on iOS, Android & ChromeOS. This seems to show the product is becoming more collaborative and managed by multiple administrators.
What does Duo add to Cisco identity and access management?
Originally Duo was a multi factor authentication solution but has been expanded by Cisco to become a full identity & access management solution. This includes single sign on, passwordless login and device trust.
Duo Essentials provides Phishing Resistant MFA using FIDO2, Verified Duo Push, SSO, Passwordless Authentication and Trusted Endpoints to ensure unmanaged/unregistered devices are excluded. Duo Advantage provides Identity Intelligence, Duo Passport, Risk Based Authentication, Adaptive Policies and Device Health Checks. Using Duo Passport will mean a user can authenticate once on a trusted device.
There is a focus on identity due to the threat intel provided by Cisco. Within their 2025 Talos Year in Review they found the majority of attacks focused on components that could authenticate the user, make access decisions and act as a trust broker. Identity Intelligence will highlight inactive accounts, over privileged accounts and inconsistent MFA across identity sources.
Where does ISE fit in Cisco network security?
ISE is the least noticeable of the three options. It focuses on lateral movement and provides centralised identity-based access control across wired, wireless and VPN. The solution can utilise 802.1X to secure authentication and MAC Authentication Bypass for non-authentication. Additionally, profiling, posture, guest and BYOD can be applied to the solution. With the Cisco TrustSec option, Security Group Tags can be used to provide identity-based policies.
As stated in the Cisco summary, ZTNA tools primarily offer application-level access control. This solution is often broad and doesn’t prevent internal threat spread. ISE is identity based and is the Policy Decision Point within the Cisco architecture.
TrustSec, endpoint analytics and fast threat containment are not available within the entry level licensing.
How do the products work together in a zero trust model?
Cisco zero trust security framework rests on three pillars: Workforce, Workload and Workplace. Duo is used in the workforce pillar. ISE and SD-Access are used in the workplace pillar. Cisco’s universal ZTNA solution combines an identity-based solution with an SSE architecture. This will go beyond simply securing remote users and will secure devices like IoT.
Let’s take an example. A contractor comes onto the campus wifi. They open a SaaS application. ISE authenticates the device and assigns a group. Duo will prompt for authentication and check device trust. Secure Access will check the web session.
Cisco has a lot of integrations with Secure Access (Duo, ISE, SD-WAN, Thousandeyes and XDR). This will ensure everything is working together. However, it is worth testing out the handovers. For example, does changing the posture on the port affect what is allowed on the cloud edge?
Where are Cisco’s enterprise access security solutions used?
Replace VPN for hybrid workforce
A ZTNA solution will cover private applications whilst a VPN as a service will cover the rest. This can be rolled out per application.
Control contractors and BYOD
Duo Trusted Endpoints will only allow access to sensitive applications using managed or registered devices. BYOD or third party hardware can be registered. Secure Access will handle unmanaged devices using clientless ZTNA.
Segmentation of campus/branches
ISE will limit communication between users and devices. This helps reduce lateral movement within campus, branches, data centres and cloud with the use of Security Group Tags.
Comply with government regulations
Secure Access for Government has FedRAMP authorisation.
How is Cisco expanding access security to AI agents?
On the 23rd March 2026, Cisco announced that Zero Trust Access was being expanded to AI agents. These can be registered in Duo IAM and mapped to a human owner. Cisco Identity Intelligence will detect Agentic and non-human identities. Secure Access will send traffic from tools through an MCP gateway. This will give granular, short-term permissions.
According to a survey conducted with key enterprise customers, 85% are experimenting with AI agents but only 5% have deployed. Jeetu Patel, President and Chief Product Officer comments “Security teams can really unlock this opportunity by making the agentic workforce safe enough to trust.” This is similar to IAM. Each AI agent will be owned by a human, have a scope and be time limited just like a contractor.
More to Know
Cisco Secure Access has integrations with Duo, Cisco SD-WAN, ISE, Thousandeyes, Cisco XDR and CSPM.
This solution will integrate with Cisco Catalyst SD-WAN and Cisco Meraki SD-WAN. It will give you a single vendor SASE option.
The architecture utilises MASQUE, QUIC, VPP and ECMP.
Cisco also offers more specific packages – DNS Defence and Secure Internet Access.
Duo offers three editions – Essentials, Advantage and Premier.
ISE will be available as a physical or virtual appliance.
Zero Trust Access has been extended to support iOS, Android and ChromeOS with Cisco Secure Client 5.1.19.
Business Fortune believes the easiest way to understand Cisco’s access security stack is to think of three decision points. Identity, Network and Cloud. Secure Access, Duo and ISE each have a decision point. Identity Intelligence will monitor underneath everything. When looking to buy Cisco enterprise security, it is useful to know where the gaps are between the three solutions. Start with the area that has the highest exposure. Test the handovers. As AI agents become part of the workforce they will be owned, scoped and timed.
FAQs
What are the main Cisco access security products?
There are four main products. Cisco Secure Access provides a cloud SSE solution, covering ZTNA, secure web gateway, CASB, Firewall as a Service and DLP. Duo provides MFA, SSO, Passwordless and device trust. Identity Services Engine provides network access control and TrustSec segmentation. Cisco Identity Intelligence provides visibility and threat detection in identity sources.
Why do enterprises choose Cisco security solutions?
They are comprehensive and have a lot of integrations. Cisco will secure your cloud edge, identity layer and network port. Secure Access will integrate with Duo, ISE, SD-WAN, Thousandeyes and XDR. They can also provide you with a single vendor SASE solution with Catalyst SD-WAN and Meraki SD-WAN. Secure Access is backed up by Talos.
How does Cisco Secure Access protect enterprise users?
It provides a zero trust solution at the cloud edge. ZTNA provides least privilege access to private applications. Secure Web Gateway and DNS will provide visibility into internet traffic. CASB and DLP will secure SaaS and Data. Legacy apps can be secured with a VPN as a service. Everything is covered using one policy.
Does Cisco Secure Access replace a VPN?
Yes. It includes a VPN as a service. This will run alongside ZTNA. This can be rolled out through the Cisco Secure Client. This means organisations can roll out applications to ZTNA gradually.
How does Cisco ISE differ to Duo?
Duo will authenticate users and verify device trust during login. ISE will authenticate users and devices when connecting to the network. This will assign segmentation policies. Duo will work on an application level whereas ISE will work on a network level.
.webp)


Comments